
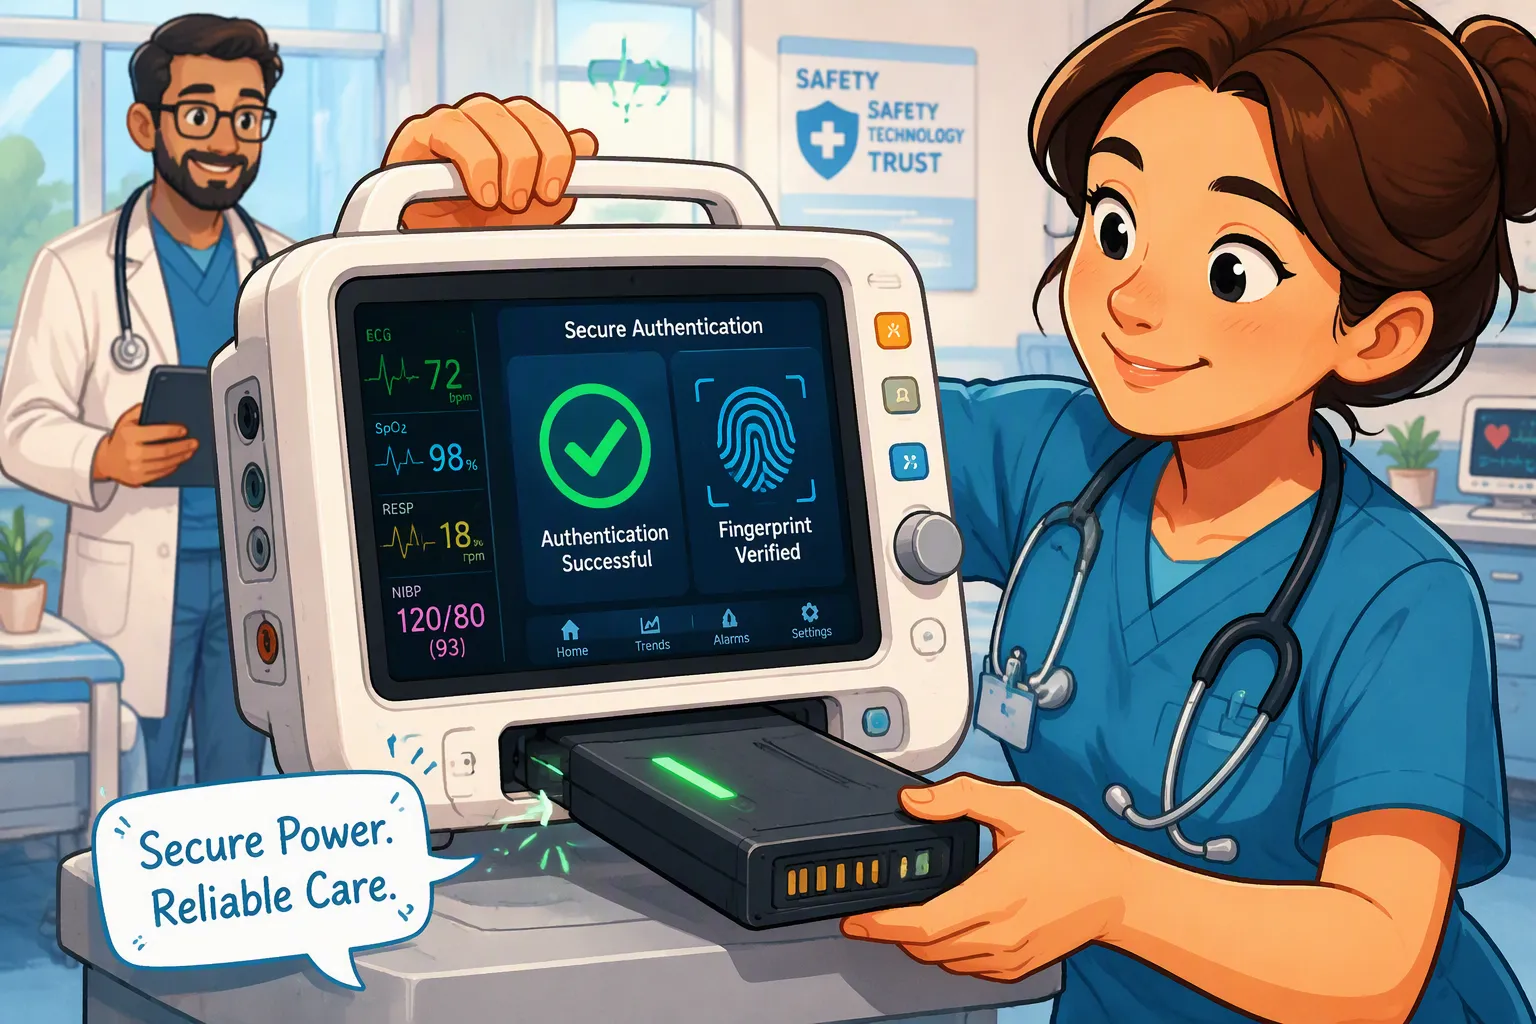
Replacement batteries for portable medical devices must do more than fit the enclosure. They need the correct electrical limits, power capability, communication behavior and service history. A counterfeit label or copied model identifier can obscure these differences.
For custom lithium battery packs, authentication can help a host verify an authorized credential. It is one part of a wider compatibility and safety strategy, not proof that every cell is healthy or that the complete device is compliant.
Quick Answer: Combine cryptographic challenge-response with an approved pack configuration, electrical protection and device-level fault handling. A readable serial number is identification, not secure authentication. Authentication failure must lead to a risk-assessed response, especially if interrupting an ongoing procedure would create a hazard.
Key Takeaways
Identity, compatibility and battery health are separate checks.
Use a reviewed authentication scheme and protect keys throughout manufacturing and service.
SMBus is a transport interface; ordinary register reads are not automatically authenticated.
Keep battery protection active regardless of authentication state.
Validate unsuccessful authentication and communication loss without assuming immediate shutdown is safe.
Part1: Define What the Device Must Verify
1.1 Distinguish Counterfeit and Incompatible Packs
A counterfeit pack misrepresents its origin or authorization. A legitimate replacement can still be incompatible with a particular device. Conversely, a correctly authenticated pack may have insufficient charge, excessive resistance or an unsupported firmware revision. Do not treat these conditions as equivalent.
Define an approved configuration covering chemistry, series count, charge voltage, current limits, temperature limits, connector pinout, mechanical retention and communication requirements. Validate these against controlled engineering records rather than accepting an untrusted chemistry string as permission to charge.
1.2 Separate the Acceptance Layers
Layer | Question | Limitation |
|---|---|---|
Identification | What model and serial number are reported? | Readable identifiers can be copied. |
Authentication | Does the pack demonstrate possession of an authorized credential? | Does not directly inspect cell quality or health. |
Compatibility | Is this configuration approved for the host? | Requires controlled configuration rules. |
Readiness and protection | Can it safely support the intended load now? | Requires measurements, diagnostics and independent protection. |
Part2: Choose an Authentication Architecture
2.1 Identification Is Not Challenge-Response
A fixed ID, resistor code or manufacturer-name register can support selection and inventory, but offers limited resistance to deliberate copying. In a challenge-response design, the host issues a fresh challenge and verifies a cryptographic response tied to a protected credential. The protocol must define message format, challenge generation, freshness, timeout and verification rules.
Do not implement authentication by simply concatenating a secret and a challenge and hashing them. Use the vendor’s specified, reviewed construction, such as a supported message authentication code or signature scheme. TI’s authentication overview distinguishes identification from cryptographic approaches. Legacy SHA-1 implementations exist, but new designs should evaluate current supported options and lifecycle security requirements rather than select SHA-1 by default.
2.2 The Bus Does Not Establish Trust
SMBus, a single-wire interface or another supported transport can carry authentication messages. The choice depends on the host and authenticator implementation. Packet error checking can detect transmission errors; it is not a cryptographic authenticity check.
Successfully authenticating a pack once does not automatically authenticate every later SOC or temperature register read. Determine whether the threat model needs integrity protection for subsequent messages, session binding or repeated verification. Define behavior after removal, reset, sleep, firmware update and bus recovery. Electrical compatibility and software interoperability still need testing even when both endpoints use SMBus.
2.3 Protect Provisioning and Credentials
Assess unique versus shared keys, secure storage, host-side protection, provisioning access, production test controls and credential revocation. A leaked fleet-wide key can affect many packs. An authentic chip transplanted into a rebuilt pack also illustrates why credential validation alone cannot establish the origin of every cell.
TI’s key-packaging tool provides one example of provisioning support for compatible gauges. The complete production process still needs controlled authorization, audit records and a recovery plan. Do not expose secrets in service logs, labels or ordinary manufacturing exports.
Part3: Coordinate Authentication with Power Safety
3.1 Keep Protection Independent
The BMS and protection circuitry must enforce qualified voltage, current and temperature limits independently of whether a handshake succeeds. Fuel gauging estimates available charge and runtime; authentication establishes a credential relationship. Neither substitutes for overcurrent, short-circuit or thermal protection.
Account for how the host powers its communication and authentication circuits before accepting a pack. Avoid unintended charging or high-load operation during initial checks, and prevent signal pins from back-powering an unpowered circuit.
3.2 Design a Safe Failure Response
For a device not yet in use, rejection may prevent starting an operation or charging an unsupported pack. During active patient care, abrupt disconnection can itself be hazardous. Assess an alarm, inhibited charging, transfer to a verified alternate source or a controlled operating restriction according to the device’s risk analysis and essential performance.
Do not silently accept a failed handshake, but do not label every timeout as counterfeiting either. Distinguish communication faults, unsupported revisions, credential failures and insufficient battery readiness. Provide useful operator messages and service records without disclosing security-sensitive details.
Part4: Validate the Complete Lifecycle
4.1 Test Positive and Negative Cases
Case | Evidence to collect |
|---|---|
Approved configurations | Correct acceptance across qualified pack, host and firmware revisions. |
Copied IDs and recorded responses | Rejection of unauthorized credentials and replay attempts within the defined threat model. |
Cold, depleted or aged pack | Reliable communication, correct readiness decisions and power transitions. |
Bus timeout, reset and partial insertion | Bounded recovery, alarms and safe source selection. |
Provisioning and firmware changes | Controlled key handling, compatibility and regression results. |
Failure during active use | Device function and fault response remain consistent with the risk controls. |
4.2 Link Security to Quality Records
Maintain traceability between pack serial number, approved BOM, cell lot, firmware, test results and credential-provisioning status. Avoid storing secret keys in routine traceability records. Define how authorized replacements, repair, revocation and end-of-life service are handled.
Authentication is not a universal requirement imposed by ISO 13485 or IEC 60601-1. Applicable quality, device safety and cybersecurity requirements depend on the product and market. A battery safety test report likewise does not validate the host’s authentication logic. Coordinate the plan with the device manufacturer and qualified reviewers.
For a new medical battery project, specify the host interface, acceptance rules, security objectives and failure response early. Discuss a custom battery solution with the engineering team before freezing the interface.
FAQ
Does authentication prove a battery is safe?
No. It verifies an authorized credential under the implemented scheme. Cell qualification, compatibility, protection, aging assessment and device validation remain necessary.
Is a serial number enough to prevent counterfeiting?
No. A readable serial number can be copied. It supports traceability but is not equivalent to cryptographic proof of possession.
Must authentication use SMBus?
No. Use the transport supported by the selected host and authenticator. Define electrical behavior and the authentication message exchange explicitly.
Should the device shut down immediately after authentication fails?
Not automatically. Select a risk-assessed response that addresses the unverified pack without creating a greater hazard during active use.
Can an authenticated pack be incompatible?
Yes. It may belong to another approved product family or have an unsupported configuration. Check compatibility separately from the credential.
How should security-related changes be controlled?
Review keys, authenticator replacements, host firmware and acceptance rules through change control. Update threat analysis and repeat affected tests, including failure handling and service compatibility.


